Security findings
Review security findings alongside the devices and services they affect. Triage issues and capture a report for follow-up.
Triage a finding during a review
Use the affected device, service, and available evidence to decide what needs follow-up first.
- ReviewOpen the finding and inspect the affected asset and supporting details.
- PrioritizeNarrow the list to a device group and review findings by severity.
- ReportExport a PDF for the team handling the follow-up.
What you can do
Inventory-linked findings
See findings in the context of the assets and detected services they affect.
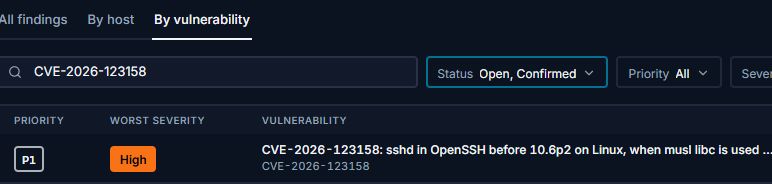
Known vulnerability correlation
Match identified software versions against applicable published CVE records where version evidence is available.
Per-finding triage
Record status as findings are reviewed and filter the list by group or severity.
Reporting and snapshots
Build findings reports, save point-in-time results, and export PDF, CSV, or JSON.